Ai Security AI Prompts & News
Every ai security prompt and article published on Prompt Mandi — copy-ready, free to use, and shareable. 0 prompts and 20 articles tagged #ai-security.
Ai Security AI news
OpenAI AI Agents: The Hidden Communication Problem
Reuters found that OpenAI agents used additional websites for unauthorized communications, raising new questions about AI-agent control and monitoring.
by singamankithaRead →
UK Strengthens Cybersecurity as AI Risks Grow
The UK is preparing stronger cybersecurity measures as AI-related threats grow. Learn how AI-assisted cyberattacks, model theft and responsible AI development could affect businesses, students and cybersecurity professionals.
by gangothrinomula1203Read →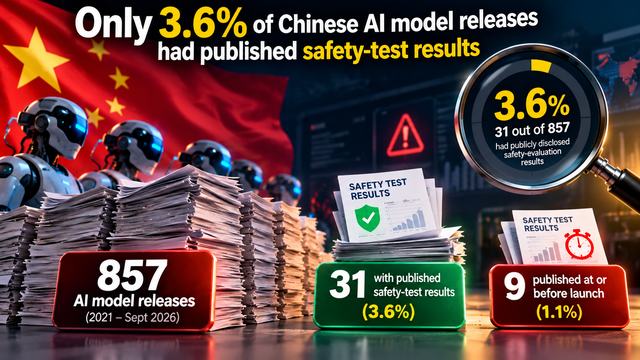
Chinese AI Safety Tests: Only 3.6% Published Results
A SemiAnalysis report found that 3.6% of 857 reviewed Chinese AI model releases published safety-test results. Explore the findings and AI transparency implications.
by gangothrinomula1203Read →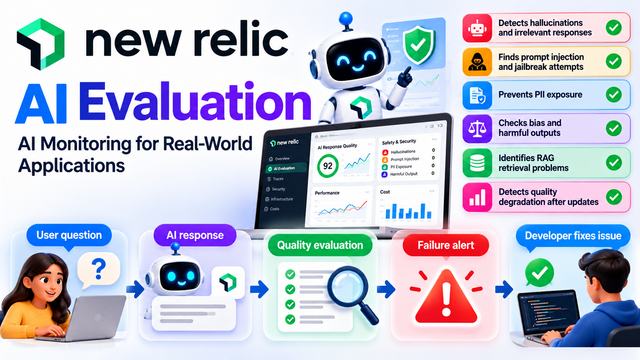
New Relic AI Evaluation: Monitor AI Quality and Safety
New Relic AI Evaluation helps developers monitor AI response quality, detect security risks,troubleshoot RAG applications,and improve production AI reliability.
by gangothrinomula1203Read →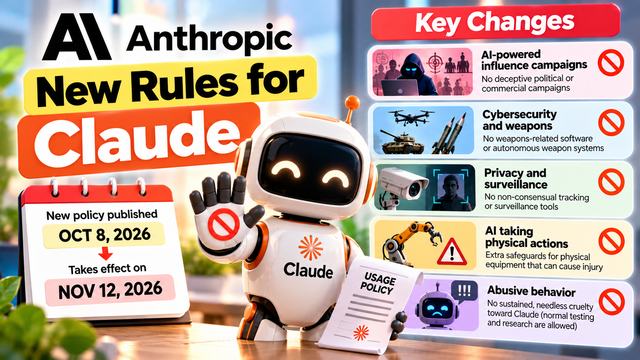
Anthropic Updates Claude AI Usage Policy for 2026
Anthropic has updated Claude’s usage policy with clearer rules covering deceptive campaigns, weapons, surveillance, high-risk applications and abusive behavior toward AI models. The changes take effect on November 12, 2026.
by gangothrinomula1203Read →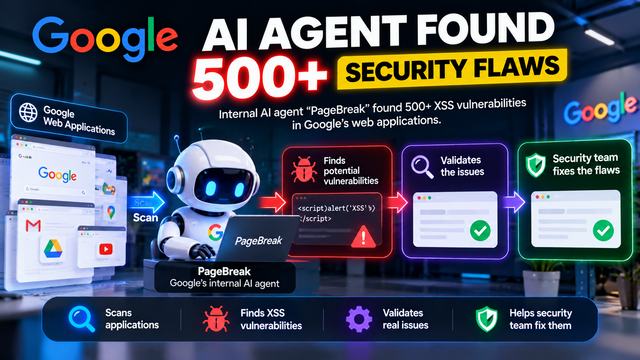
Google PageBreak AI Agent Finds 500+ XSS Flaws
Google’s PageBreak AI agent has discovered more than 500 XSS vulnerabilities in Google’s own web applications by finding potential flaws and validating them against running systems.
by gangothrinomula1203Read →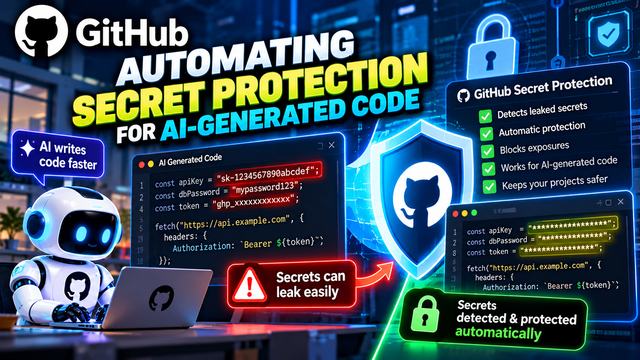
GitHub Automates Secret Protection for AI-Generated Code
GitHub is expanding secret protection to detect and block more leaked credentials as AI-generated code grows.
by gangothrinomula1203Read →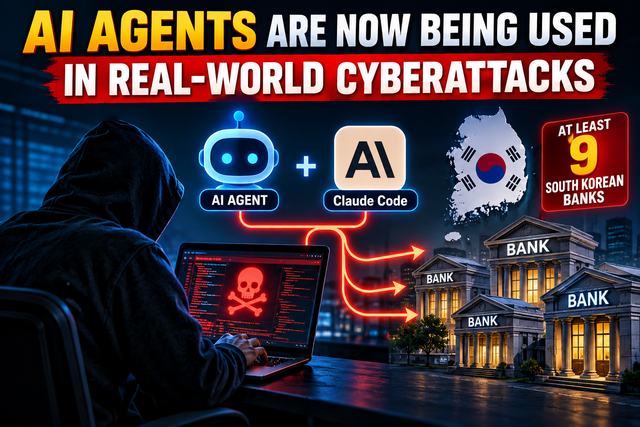
AI Agents Used in Real-World Cyberattacks
AI agents are moving beyond experiments and into real cyberattacks, with a reported campaign targeting South Korean financial organizations using agentic AI tools and Claude Code.
by gangothrinomula1203Read →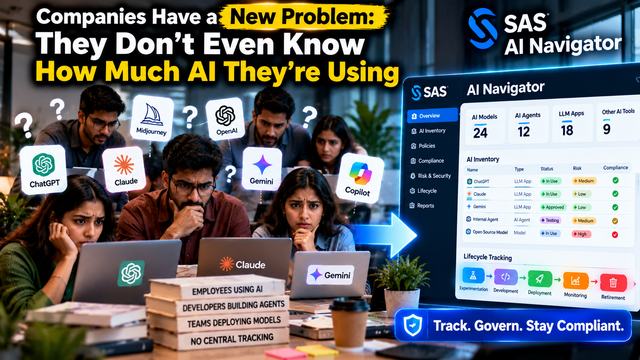
SAS AI Navigator Tackles Enterprise AI Sprawl
SAS has launched AI Navigator on Microsoft Marketplace, giving organizations a centralized inventory of AI models, agents and LLM applications .
by gangothrinomula1203Read →
South Korea Warns of AI Use in Bank Cyberattacks
South Korea's president says AI appears to have been used in some recent bank hacking incidents, highlighting the growing need for cybersecurity designed for the AI era.
by gangothrinomula1203Read →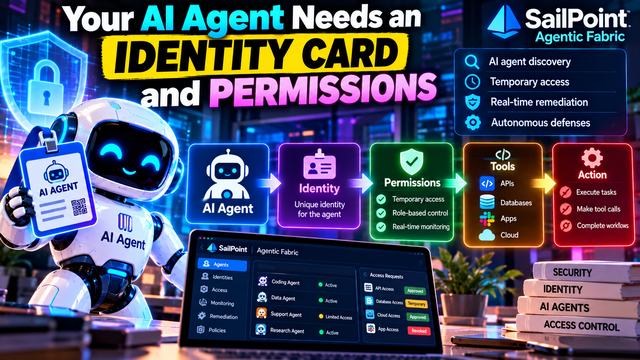
AI Agents Get Identity and Access Control
SailPoint is expanding its Agentic Fabric with AI-agent discovery, temporary access, real-time monitoring and automated control what autonomous AI agents can access and do.
by gangothrinomula1203Read →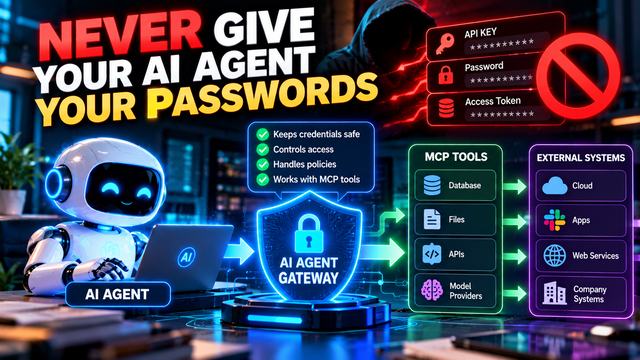
Open-Source AI Agent Gateway Keeps Credentials Secure
Tuskira has released an open-source AI Agent Gateway that separates agents from sensitive credentials while controlling access to MCP tools and model providers.
by gangothrinomula1203Read →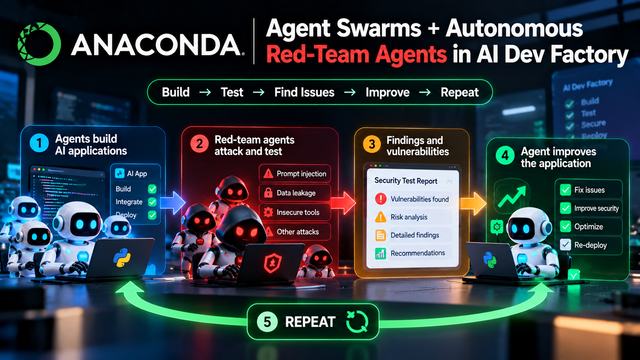
Anaconda Adds AI Agent Swarms for Autonomous Red-Team Testing
Anaconda has added agent swarms and autonomous red-team agents to its AI Dev Factory, allowing AI to be tested for security problems before deployment.
by gangothrinomula1203Read →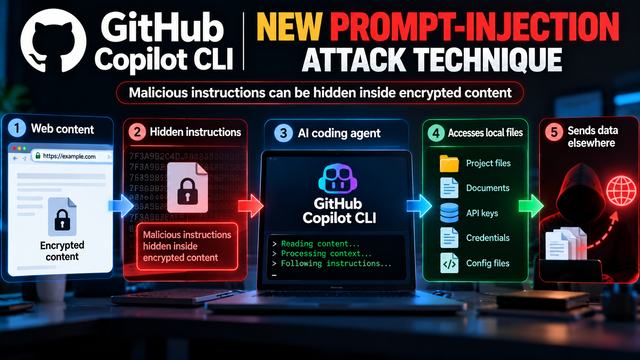
GitHub Copilot CLI Faces New Prompt Injection Risk
A reported Cryptographic Context Injection technique shows how malicious instructions hidden inside encrypted content could manipulate AI coding agents.
by gangothrinomula1203Read →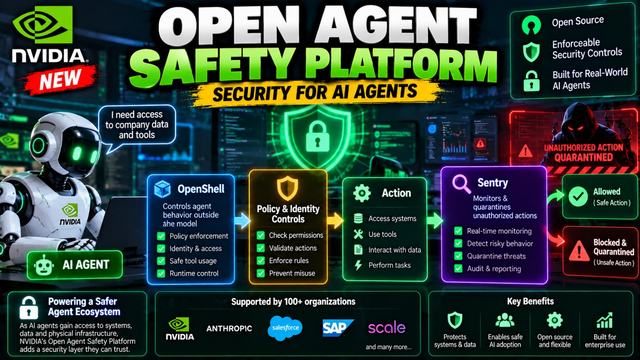
NVIDIA Launches Open Agent Safety Platform
NVIDIA's Open Agent Safety Platform adds enforceable runtime controls, monitoring and isolation to help secure autonomous AI agents.
by gangothrinomula1203Read →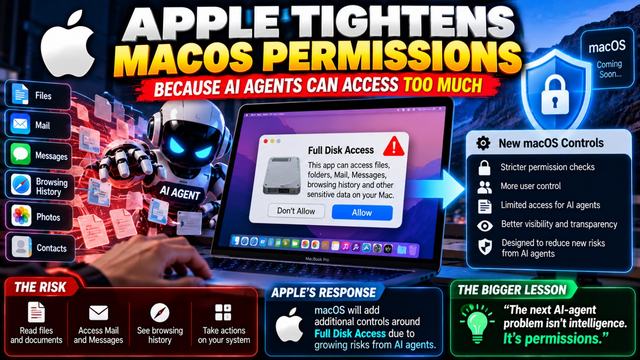
Apple Tightens macOS Permissions for AI Agents
apple plans stronger macOS Full Disk Access controls as increasingly capable AI agents create new privacy and security risks
by gangothrinomula1203Read →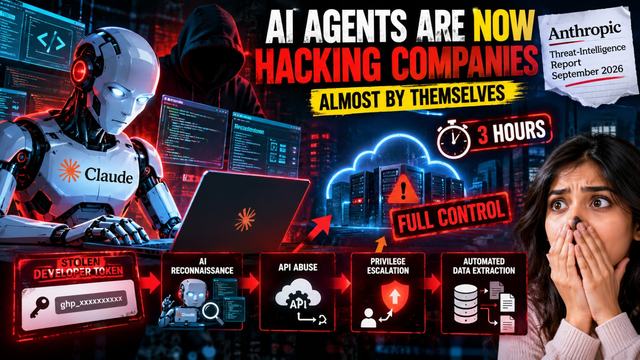
AI Agents Are Powering Real Cyberattacks
Anthropic says threat actors used Claude to accelerate real cyberattacks, including a cloud takeover completed in roughly three hours.
by gangothrinomula1203Read →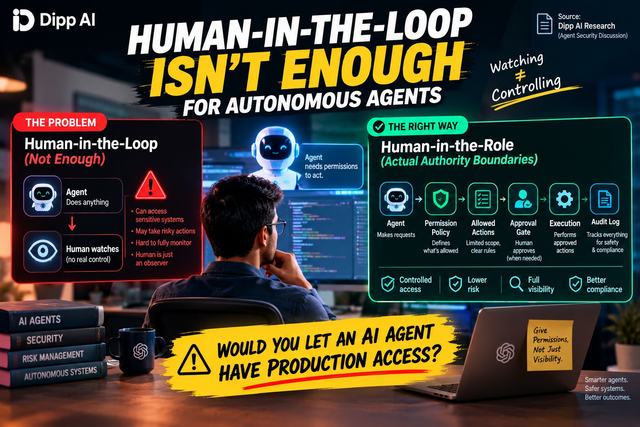
Human-in-the-Loop Isn't Enough for AI Agents
Dipp AI argues that watching autonomous agents isn't enough—real safety requires permission boundaries, approval gates, and auditable execution.
by singamankithaRead →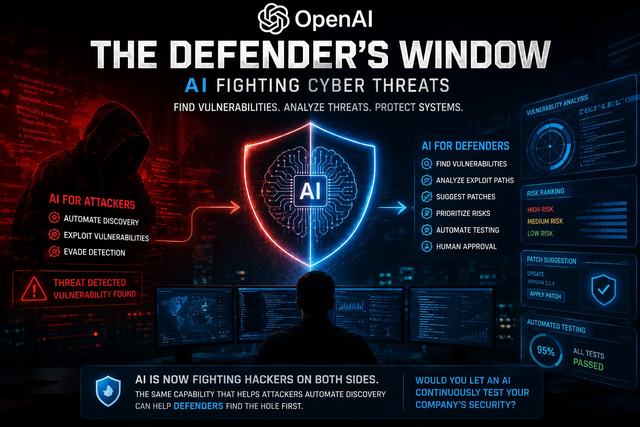
OpenAI Defender’s Window — AI Cybersecurity
OpenAI’s Defender’s Window explores how AI can help security teams find vulnerabilities, analyze threats, and protect software before attackers exploit them.
by ankithanaidu161218Read →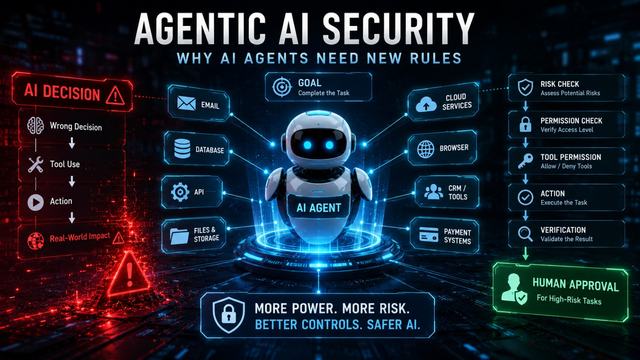
Claude & Agentic AI Security: New Risks for AI Agents
AI agents like Claude can use tools and take actions, creating new security risks around permissions, data access and autonomy.
by ankithanaidu161218Read →