Google PageBreak AI Agent Finds 500+ XSS Flaws
Google’s PageBreak AI agent has discovered more than 500 XSS vulnerabilities in Google’s own web applications by finding potential flaws and validating them against running systems.
Source: https://blog.google/security/agentic-hacks-real-proofs-inside-googles-pagebreak-project/
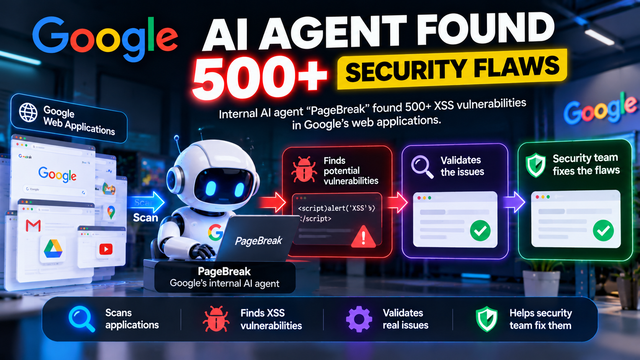
Google PageBreak AI Agent Finds 500+ XSS Flaws
Google is using an AI agent to actively search for security vulnerabilities inside its own web applications — and the results show how far AI-powered cybersecurity is moving.
The AI agent, called PageBreak, was developed by Google’s Product Security team to test Google’s first-party web applications. According to Google, PageBreak has uncovered more than 500 Cross-Site Scripting (XSS) vulnerabilities across its web applications.
This is important because PageBreak is not simply asking an AI model to look at source code and guess where a vulnerability might exist. Google designed the system around a discovery-and-validation process.
The basic workflow looks like this:
AI agent → searches applications → identifies possible vulnerability → validates the finding → security team investigates and fixes it
That validation step is one of the most interesting parts of the project.
What is PageBreak?
PageBreak is an internal AI security agent created to help Google scale vulnerability discovery. Google began experimenting with the project as a pilot in November 2025 and moved it into a full-fledged project in January 2026.
The goal is to let an AI agent investigate applications at a much larger scale while reducing repetitive manual work for security researchers.
Google says PageBreak primarily uses Gemini models, including Gemini 3.1 Pro and Gemini 3.5 Flash, although the system is designed to work with different models.
But simply using a powerful AI model isn't enough for cybersecurity.
AI systems can sometimes produce convincing but incorrect vulnerability reports. Security teams could end up spending more time investigating false alarms than fixing real problems.
Google's PageBreak approach attempts to solve this problem by giving the agent access to specialized validation tools.
The important difference: finding vs proving
Imagine an AI agent examines a website and says:
“I think this page might contain an XSS vulnerability.”
That is only a hypothesis.
PageBreak takes the next step. Google explains that potential findings are passed to specialized validators that attempt to confirm whether the vulnerability can actually be exploited in a running environment.
For XSS vulnerabilities, the validation process can use a specific JavaScript payload and monitor the application to determine whether the injected code actually executes.
This creates a much stronger security workflow:
Find → Test → Confirm → Report
Instead of flooding security engineers with hundreds of theoretical problems, the system attempts to focus attention on vulnerabilities that can be demonstrated.
Google describes this deterministic validation approach as producing a near-zero false-positive rate for the validated findings.
What are XSS vulnerabilities?
XSS stands for Cross-Site Scripting.
An XSS vulnerability can allow malicious script content to be executed in a user's browser through a vulnerable web application. Depending on the situation, this can create serious security and privacy risks.
The fact that PageBreak found more than 500 XSS vulnerabilities across Google's first-party web applications demonstrates the scale at which an automated security agent can operate.
However, this does not mean that Google had 500 websites hacked.
It means the system identified vulnerabilities in Google's web applications that could potentially be exploited and used validation to confirm findings.
That distinction is important when discussing this story.
AI agents are becoming security researchers
The bigger story is not only the number 500.
It is the changing role of AI agents in cybersecurity.
Traditional security scanners are already capable of finding many types of vulnerabilities. AI agents add another layer because they can reason through applications, follow code paths, use security tools and investigate potential attack surfaces.
Google says PageBreak can leverage its large codebase, security signals and existing scanning infrastructure to investigate applications at scale.
This is very different from using AI only as a coding assistant.
Instead of:
Developer → prompts AI → AI writes code
the security workflow becomes:
AI agent → investigates application → searches for weaknesses → validates findings → security team reviews
That is a much more autonomous use of AI.
Google wants AI to help fix the vulnerabilities too
Finding vulnerabilities is only half of the problem.
After a security issue is discovered, developers still need to understand the root cause, create a fix, test it and deploy the change safely.
Google says PageBreak is collaborating with other agentic security initiatives, including CodeMender, with the longer-term goal of connecting vulnerability discovery with automated fix generation.
That could create a future workflow where AI systems continuously search for vulnerabilities, propose fixes and validate those fixes before human engineers give final approval.
The human role would shift from manually searching for every issue toward reviewing high-confidence findings and proposed solutions.
Why this matters for Indian developers and businesses
This trend is especially relevant as Indian startups, banks, SaaS companies and digital platforms increasingly depend on large web applications and AI-powered systems.
Security teams often have limited time compared with the number of applications, APIs and code changes they need to monitor.
AI agents could help automate repetitive security testing and allow security engineers to spend more time on complex vulnerabilities and architecture-level risks.
For students and developers, the lesson is also important: AI-assisted development should not stop at generating code.
The next generation of development workflows will increasingly include AI-powered testing, vulnerability discovery, code review and automated remediation.
But there is an important limitation.
Organizations should not give an autonomous agent unrestricted access to production systems simply because the agent is capable of finding vulnerabilities. Security testing needs controlled environments, permissions, logging, validation and human oversight.
Google's PageBreak project demonstrates the potential of AI for defensive cybersecurity, but it also highlights why autonomous security agents need strong guardrails.
The bigger picture
Google's PageBreak is another example of AI moving from passive assistance toward active work.
The interesting part isn't simply that an AI model can recognize an XSS pattern.
The interesting part is that an agent can investigate an application, develop a hypothesis, use specialized tools, test the hypothesis against a running environment and provide evidence for a security team.
That changes the economics of vulnerability research.
Instead of security teams manually checking every possible weakness, AI agents can potentially perform continuous investigation at machine scale while humans focus on the findings that matter most.
Google's 500+ XSS vulnerabilities are therefore more than just a large number. They are a signal that AI agents are becoming serious tools for defensive cybersecurity — and that the future of software security may involve AI continuously attacking applications so humans can make them safer.
For developers and businesses, the message is simple:
AI isn't only becoming better at building software. It's becoming better at trying to break it too.