NVIDIA CEO Says Cybersecurity Is cinematical AI's Next Big Application
Jensen Huang says AI-powered cybersecurity could become a major market, with systems finding vulnerabilities and defending networks continuously.
By @admin
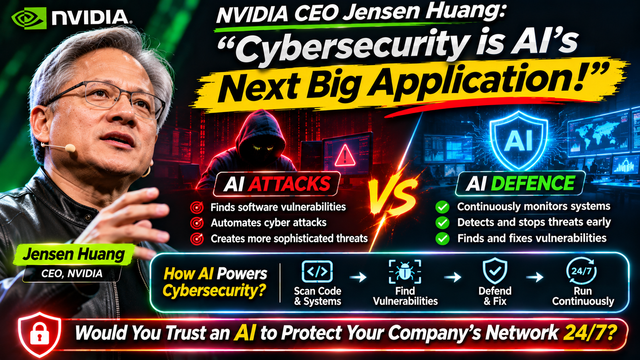
NVIDIA CEO Jensen Huang Says Cybersecurity Is AI's Next Big Application
Artificial intelligence has already transformed software development. Developers are using AI assistants to write code, find bugs, explain complex systems and automate repetitive programming tasks.
But NVIDIA CEO Jensen Huang believes another major opportunity is emerging from this progress: cybersecurity.
Speaking at the Goldman Sachs Communacopia + Technology Conference in San Francisco on September 10, 2026, Huang said cybersecurity would likely become AI's next major use case after coding.
His argument is straightforward. If AI can write code, it can also help find weaknesses in code. And if it can identify vulnerabilities, it can potentially help security teams fix them.
This could change how organisations protect their networks, applications and digital infrastructure.
But there is another side to the development. The same AI capabilities that help defenders identify security weaknesses could also help attackers discover and exploit them.
The result could be a new cybersecurity environment in which both attacks and defences become increasingly automated.
1. Jensen Huang's prediction: Cybersecurity after coding
AI-powered coding tools have become one of the most visible applications of artificial intelligence.
Developers can ask an AI assistant to generate functions, explain code, identify errors and suggest improvements. Tasks that previously required significant manual effort can now be completed much faster.
During his Goldman Sachs conference appearance, Jensen Huang connected this development to cybersecurity.
He explained that bug finding is a natural extension of coding, and cybersecurity is a much larger market built around identifying and fixing software weaknesses.
His key prediction was that cybersecurity would likely become AI's next major use case.
Why does this matter?
Modern businesses depend on software. Banks, hospitals, e-commerce platforms, government services and cloud infrastructure all rely on applications, databases and connected networks.
Every additional software system creates another area that needs protection.
As software development becomes faster, security teams may face an increasing number of changes to inspect and protect.
AI could help organisations deal with that growing workload.
2. Why AI is a natural fit for cybersecurity
Cybersecurity involves several tasks that AI systems are increasingly capable of supporting.
These include analysing large amounts of information, identifying unusual patterns, comparing software behaviour, reviewing code and helping people investigate complex problems.
Consider a company that operates hundreds of applications and servers.
Its security team may need to examine:
- Network activity
- Login attempts
- Application logs
- Software updates
- Suspicious files
- Access permissions
- Newly discovered vulnerabilities
- Unusual user behaviour
Reviewing all this information manually can be difficult, particularly when threats emerge continuously.
AI can help process large amounts of security data, identify patterns and highlight activity that deserves attention.
For example, an AI-powered security system could detect an unusual login pattern, connect it with other suspicious events and prepare an investigation summary for a security analyst.
Instead of manually searching through thousands of records, the analyst could begin with a prioritised report.
This does not mean AI will always identify the correct threat. It means AI can potentially help security teams process information faster and focus their attention where it is needed.
3. AI-powered defence: Security that operates continuously
One of Huang's most interesting points was that AI cybersecurity systems could operate continuously rather than waiting for a human to provide a prompt.
Traditional security tools often depend on predefined rules, alerts and human investigation.
A security analyst might receive an alert, investigate the event, collect evidence and decide what action should be taken.
AI agents could automate parts of this process.
A continuous defensive workflow could look like this:
Monitoring: The system observes authorised network and application activity.
Detection: AI identifies unusual patterns or behaviour that may indicate a security problem.
Investigation: The system gathers relevant information and connects related alerts.
Recommendation: It prepares possible responses for the security team.
Response: Approved actions can be taken automatically within clearly defined permissions.
Verification: The system checks whether the issue has been resolved and records what happened.
This could reduce the time between detecting a problem and responding to it.
However, continuous operation does not mean an AI system should receive unlimited access to an organisation's infrastructure.
Sensitive actions, such as shutting down important services, changing critical permissions or modifying production systems, may require human approval.
The objective should be faster security with controlled authority, not uncontrolled automation.
4. Red teaming versus blue teaming: AI on both sides
To understand the future of AI cybersecurity, it helps to know two important terms: red teaming and blue teaming.
Red teaming focuses on finding weaknesses by testing systems from an attacker's perspective.
Security professionals use controlled testing to discover vulnerabilities before malicious actors can exploit them.
Blue teaming focuses on defending systems.
Blue teams monitor infrastructure, investigate suspicious activity, strengthen security controls and respond to incidents.
AI can potentially improve both sides.
On the red-team side, AI can help security professionals review code, identify weaknesses and automate authorised security testing.
On the blue-team side, AI can help detect suspicious activity, analyse alerts, investigate incidents and recommend defensive actions.
This creates an interesting situation.
The same general capability—analysing software and identifying weaknesses—can support both offensive security testing and defensive protection.
That is why access controls, usage restrictions and responsible deployment matter.
AI cybersecurity is not automatically defensive simply because a company sells it as a security product.
The permissions and purpose of the system determine what it can do.
5. NVIDIA is already working with cybersecurity companies
Huang's comments are not just a prediction about a distant opportunity. NVIDIA is already developing partnerships in this area.
One important example is its work with CrowdStrike.
On September 1, 2026, NVIDIA and CrowdStrike announced their work on SafeMind, an agentic cybersecurity system designed to support continuous security operations.
The system combines CrowdStrike's cybersecurity technology and models with NVIDIA's Nemotron open models.
The companies described a continuous approach in which AI systems support both red-team testing and blue-team defence.
The idea is to help security teams identify weaknesses and strengthen protection through repeated testing and improvement.
NVIDIA has also highlighted partnerships involving Cisco and Palantir.
These partnerships show that the cybersecurity opportunity is not limited to one chatbot or one security feature. Companies are exploring AI infrastructure, specialised models and agent-based systems for larger enterprise security operations.
For NVIDIA, cybersecurity is also a business opportunity because advanced AI security systems require computing infrastructure.
The company supplies the hardware and software platforms used to build and operate many of these systems.
6. The danger: AI can help attackers too
There is an important issue that cannot be ignored.
If AI makes it easier to identify software vulnerabilities, that capability can be used by attackers as well as defenders.
Cybercriminals could potentially use AI to support phishing campaigns, analyse stolen information, discover weaknesses or automate parts of malicious activity.
AI can also help attackers produce convincing messages, translate scams into different languages and adapt their tactics.
This creates an arms race.
Defenders want AI systems that identify threats faster. Attackers want AI systems that help them find weaknesses faster.
The advantage may go to the organisation that can detect, understand and respond to threats more quickly.
But there is no guarantee that defenders will always win.
AI-powered cybersecurity therefore requires more than deploying an AI agent. Organisations also need strong identity controls, secure software development, network segmentation, backups, monitoring and trained security professionals.
AI should strengthen these protections, not replace them.
7. What does this mean for Indian businesses?
India's digital economy depends on banking platforms, payment systems, online marketplaces, healthcare applications, cloud services and thousands of software companies.
As businesses adopt AI, they also need to think about the security of the systems they build and operate.
For example, an Indian e-commerce company could use AI to analyse unusual account activity and help identify suspicious transactions.
A software startup could use AI-assisted code review to identify potential vulnerabilities before releasing an update.
A bank could use AI to help security analysts investigate unusual access patterns.
A small business could use automated monitoring to receive alerts about suspicious login attempts and exposed services.
These are potential applications, not guarantees that AI will prevent every attack.
Businesses must also consider the privacy and security of the data they share with AI tools.
Sensitive customer information, passwords, internal source code and confidential business records should not be sent to unapproved services.
For smaller organisations, the practical starting point is to improve basic security practices and then introduce AI where it provides a measurable benefit.
8. Will AI replace cybersecurity professionals?
Not necessarily.
AI may automate repetitive analysis and support faster investigations, but cybersecurity involves more than finding technical errors.
Security professionals need to understand business risks, legal requirements, system architecture and the consequences of taking action.
An AI system might identify suspicious activity, but a human expert may need to decide whether shutting down a service would create a bigger problem.
An AI tool may flag a software vulnerability, but developers still need to verify its severity and determine the correct fix.
The likely direction is greater collaboration between security professionals and AI systems.
Professionals who understand both cybersecurity fundamentals and AI automation may become particularly valuable.
For students interested in this field, useful skills include networking, operating systems, programming, cloud security, vulnerability assessment, security monitoring and AI fundamentals.
Learning how to use AI tools is useful, but understanding the underlying security concepts is essential.
9. The future: A continuous AI-versus-AI cybersecurity race
Jensen Huang's prediction highlights a major shift in the technology industry.
AI coding tools are changing how software is created. That creates new opportunities for identifying bugs, testing applications and protecting the systems that depend on software.
Cybersecurity could become one of the most important commercial applications of AI because digital threats do not operate only during business hours.
Organisations need protection around the clock.
AI agents could help monitor systems continuously, investigate suspicious behaviour and support faster defensive responses.
At the same time, malicious actors may also use AI to increase the speed and scale of their operations.
The outcome will depend on how these systems are designed, restricted, tested and deployed.
For NVIDIA, this creates an opportunity to expand its AI infrastructure and partnerships into a major technology market.
For businesses, it creates a reason to rethink cybersecurity strategies.
For developers and students, it creates another important area in which AI and technical expertise will increasingly overlap.
The big question is no longer just whether AI can find software vulnerabilities. It is whether AI can help organisations fix them faster than attackers can exploit them.